Security Review Agents
Combined seven scanning tools with eight specialist AI reviewers to investigate security findings and filter noise before issues reach engineers.
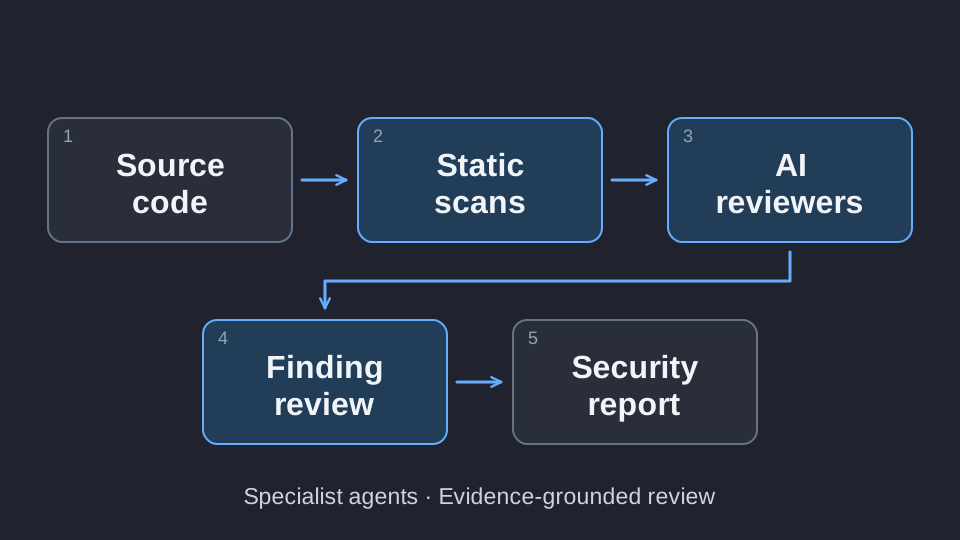
Specialist review with a noise filter · Role: Architect & Engineer
Architecture
- Seven static analysis and dependency tools run before model analysis.
- Eight CWE-scoped agents review distinct security domains.
- A judge considers reachability, existing controls, and test context before findings are filed.
Results & scale
- Seven deterministic scanning tools
- Eight specialist agents with an 80% default confidence gate
Technology stack
- LangGraph
- Python
- Semgrep
- Bandit
- GitHub
My contribution
Original specialist orchestration, finding review, and issue integration around existing scanning tools.